
AI-SAFE CLOUD-NATIVE APPLICATION SECURITY
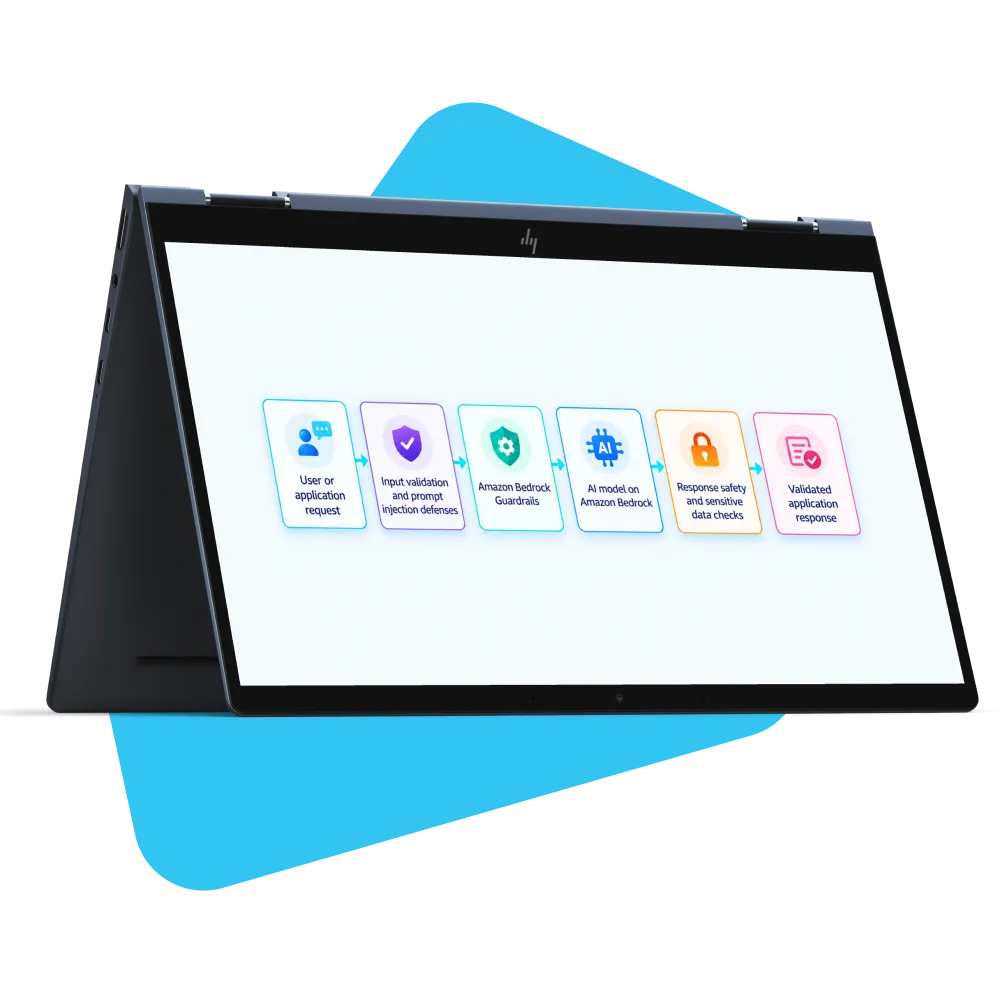
Creole Studios designed a cloud-native AI security framework to protect applications against both AI-specific and infrastructure-level risks. The solution combines behavioral guardrails, cloud security controls, restricted agent permissions, and human approval checkpoints to help AI applications operate safely in production.
 Remote
5K – 10K USD
1.5 - 2 Months
Web
About the Project
Building Secure and Predictable Cloud-Native AI Applications
The project focused on creating a structured security approach for AI applications running in cloud environments.
The solution addressed risks such as prompt injection, sensitive data exposure, hallucinations, unsafe agent actions, excessive IAM permissions, insecure networking, and secrets management.
Creole Studios designed layered safeguards that could support new applications, existing-system assessments, security remediation, and ongoing AI safety validation.

Project Challenges
The key challenge was securing both the AI behavior layer and the underlying cloud infrastructure without limiting legitimate application functionality.


AI-Specific Security Risks : Prompt injection, hallucinations, data leakage, and unsafe tool execution created risks beyond traditional application security.
Excessive Agent Permissions : Autonomous agents required tightly controlled access to APIs, data, and external systems to prevent unintended actions.
Cloud Infrastructure Exposure : IAM policies, secrets, networking, and service configurations needed to follow least-privilege and secure deployment principles.
Changing AI Behavior : Model, prompt, tool, and workflow updates could introduce new risks even when the underlying application architecture remained unchanged.


How Did We Help?
We Built Layered Security Across AI and Cloud Infrastructure
AI Threat Modeling
Behavioral Guardrails
Agent Action Boundaries
Human Approval Gates
Cloud Security Hardening
Prompt Injection Protection
Security Remediation

The outcome
The AI-safe cloud-native framework established a more structured approach to securing AI applications before and after production deployment.
Key Outcomes
- Clearer AI threat identification
- Tested behavioral guardrails
- Restricted agent permissions
- Human control over sensitive actions
- Stronger cloud security practices
- Improved production-readiness evidence
- Repeatable safety validation as AI systems evolve
The solution helps organizations adopt AI capabilities while maintaining clearer operational boundaries across both model behavior and cloud infrastructure.

Chris Auger
“AI application security requires protection at two levels: how the AI behaves and what the underlying cloud environment allows it to access or execute.”